Zero-Trust Security
Enterprise Cloud Application & Infrastructure Security
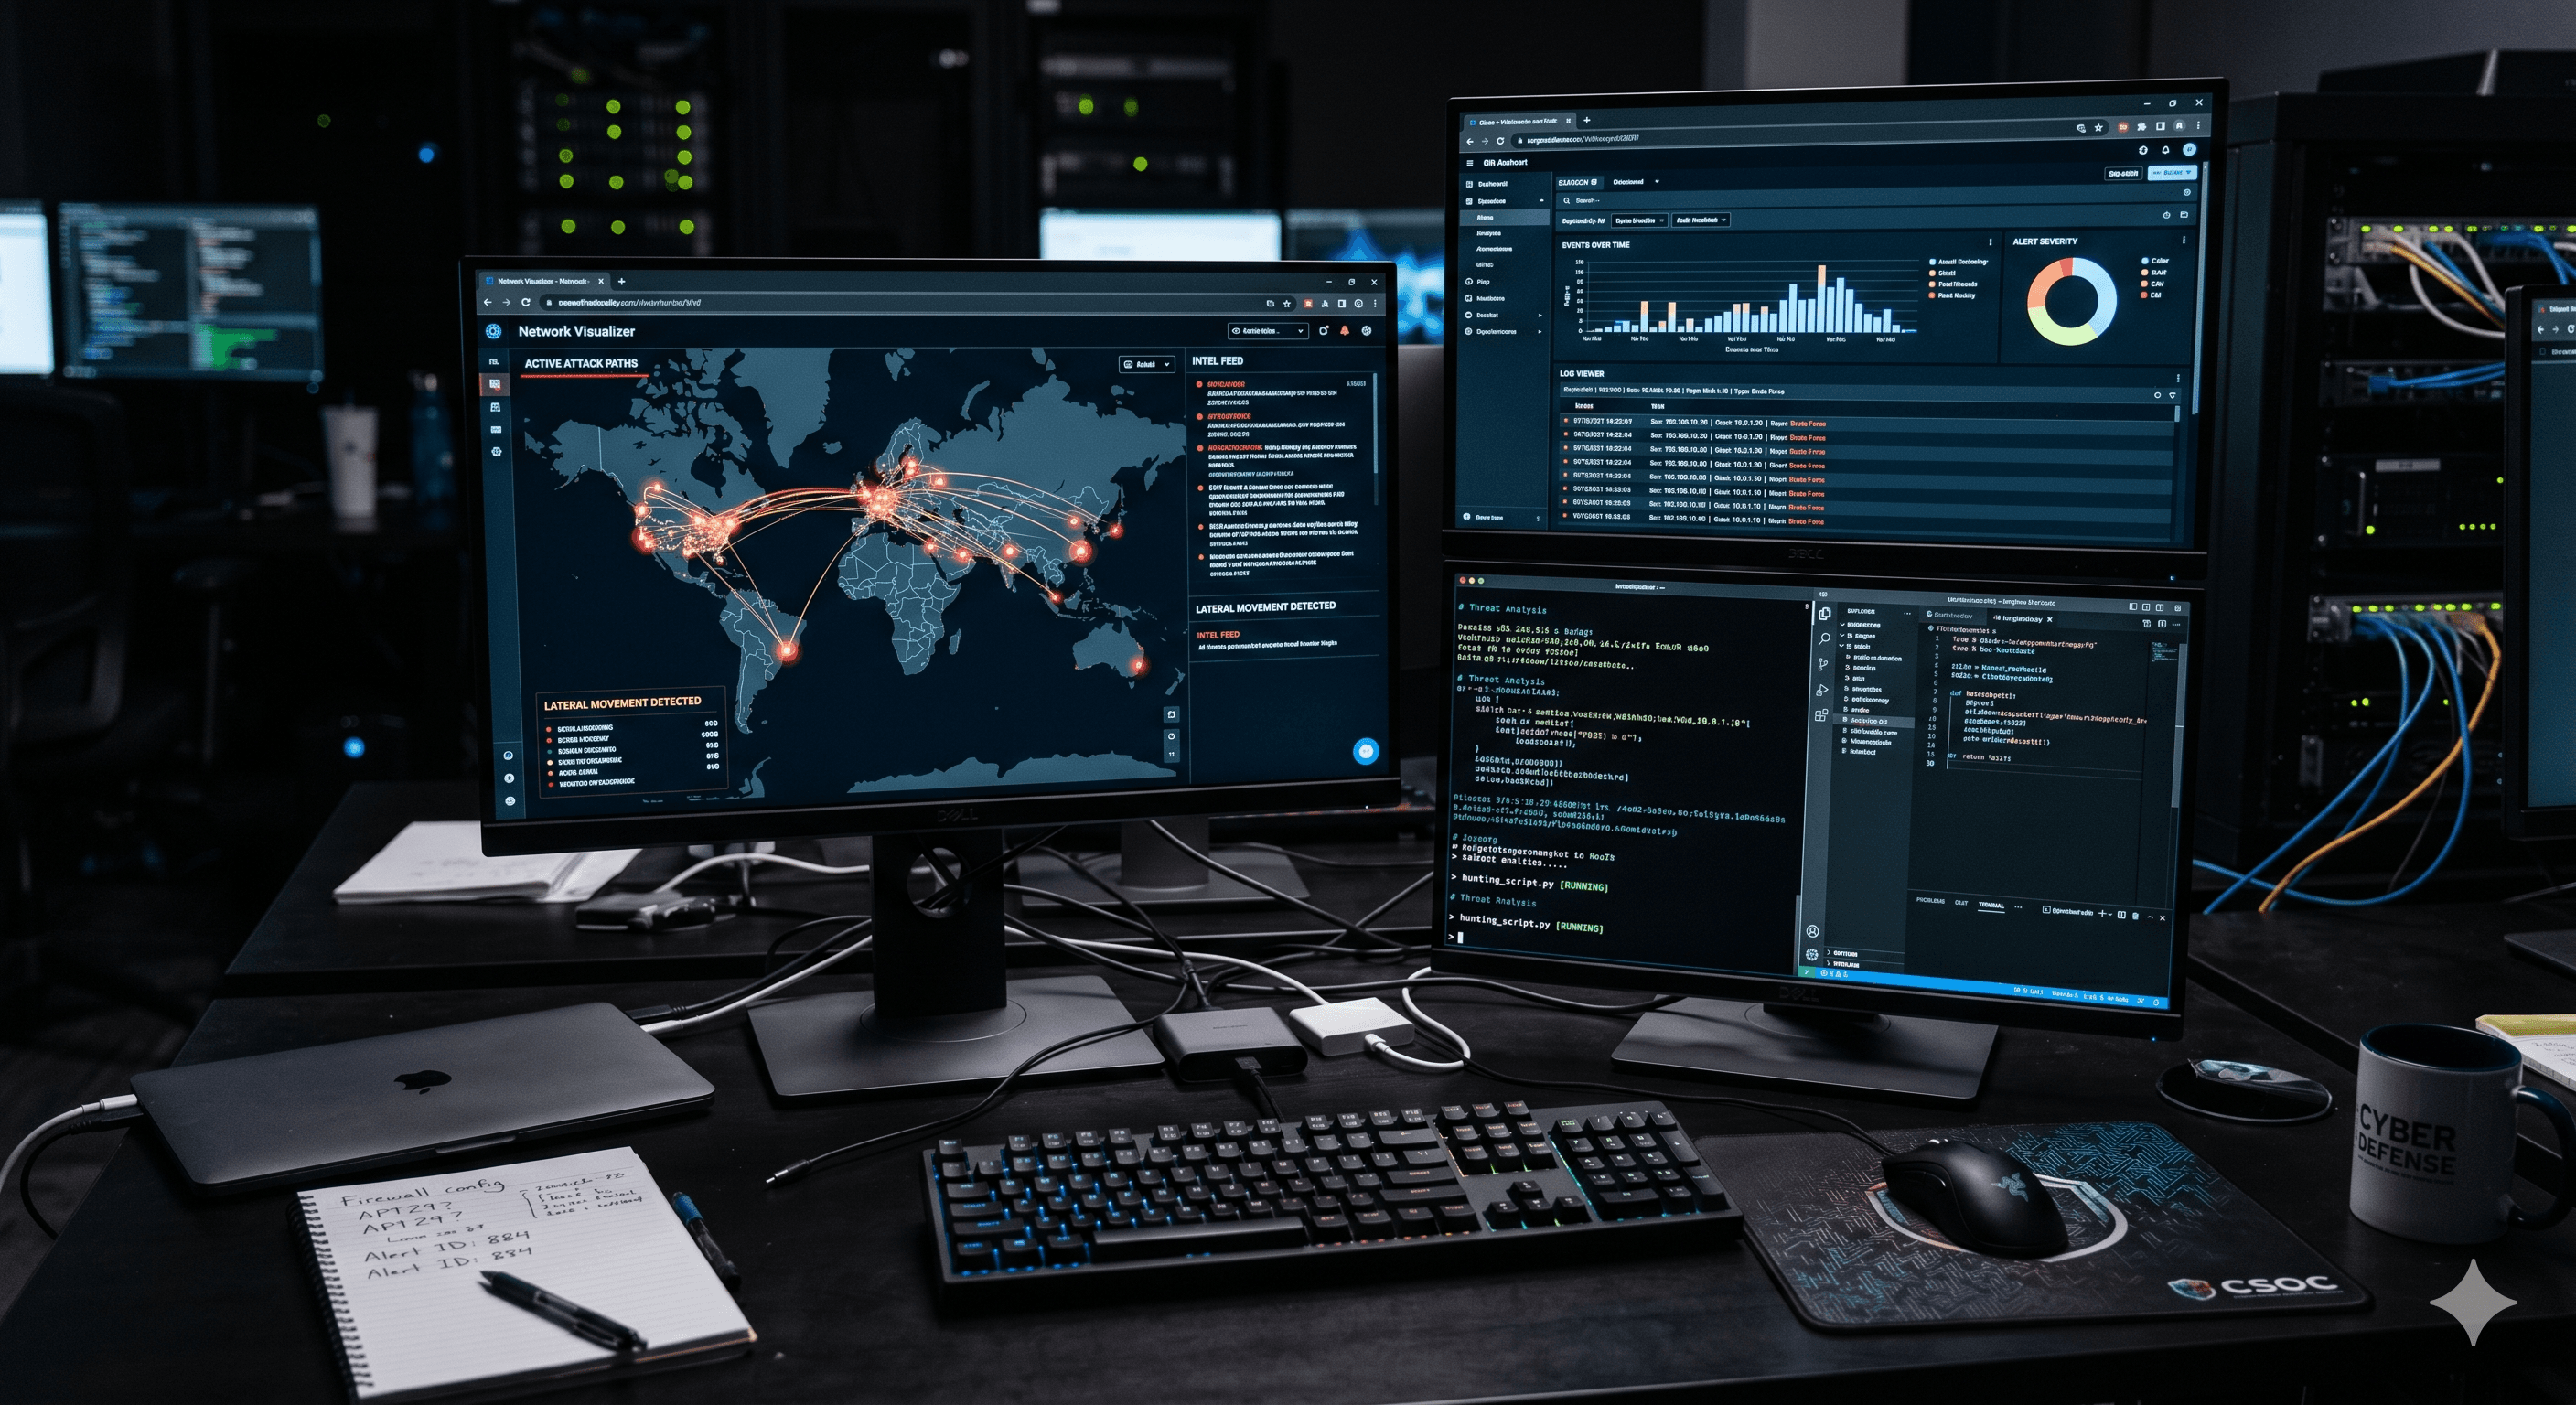
Protect critical digital assets, customer data, and cloud workloads with penetration testing, automated vulnerability monitoring, and regulatory compliance frameworks.
Zero
Breach tolerance
SOC 2
Compliance alignment
24/7
Threat monitoring
OWASP
Top 10 fortified
Production Standard
Verified Engineering
A complete engineering experience
Designed around quality, architecture, and scalable growth.
Our Cybersecurity & Cloud Protection practice unifies architectural rigor, clean codebase standards, and transparent sprint reporting into one cohesive engagement. We build software that performs under heavy load while keeping delivery schedules predictable.
01Penetration Testing & Vulnerability Scans
02Cloud Infrastructure Hardening (AWS/GCP/Azure)
03Zero-Trust Network & IAM Architecture
04Automated Continuous Security Pipelines
Built for modern businesses
What is Cybersecurity & Cloud Protection?
For startups For scaling enterprises
Cybersecurity Services protect modern enterprises against evolving threats. We combine offensive security testing with defensive cloud architecture to seal vulnerabilities, protect databases, and ensure compliance with ISO 27001, SOC 2, and GDPR.
Business valueAccelerated product launch cycles, predictable engineering velocity, and measurable operational efficiency.
Technical valueZero-debt architectures, hardened cloud security, automated test coverage, and transparent code ownership.
Business advantages
Why Choose Our Cybersecurity & Cloud Protection?
Regulatory Compliance & Customer Trust
Secure DevSecOps CI/CD Integration
Comprehensive Disaster Recovery Readiness
Core engineering capabilities
Everything needed to build and scale with confidence.
01↗
Web & Mobile Application Penetration Testing
02↗
Cloud Security Posture Management (CSPM)
03↗
Identity & Access Management (IAM) Hardening
04↗
Automated Dependency & Container Vulnerability Scanning
05↗
API Security & Rate-Limiting Gateways
06↗
Incident Response Planning & Disaster Recovery
Simple, connected delivery framework
How It Works
A clear, guided journey from technical discovery to production deployment and proactive scaling.
Step 01
Threat Modeling & Attack Surface Audit
Identify exposed endpoints, misconfigured cloud storage, and architectural weak spots across your infrastructure.
Step 02
Penetration Testing & Vulnerability Discovery
Ethical security researchers simulate real-world attacks against your APIs, databases, and client applications.
Step 03
Remediation & Infrastructure Hardening
We work directly with your engineering team to patch code flaws, implement cryptographic safeguards, and enforce least-privilege IAM.
Step 04
DevSecOps Automation & CI/CD Security
Embed automated static analysis (SAST) and dynamic analysis (DAST) directly into your pull request pipelines.
Step 05
Compliance Documentation & Continuous Monitoring
Prepare audit-ready reports for ISO 27001 / SOC 2 certification and activate 24/7 cloud telemetry alerting.
Engineered for your business model
Where Cybersecurity & Cloud Protection creates value
Tailored delivery strategies for growing teams that demand high reliability, clean architectural standards, and fast turnaround.
 01
Application Scope
Fintech & Payment Gateway Security
Strategic Value
Fintech & Payment Gateway Security
Ensure PCI-DSS compliance, tokenize sensitive cardholder data, and safeguard financial transaction ledgers.
 02
Application Scope
Healthcare & Sensitive Records Protection
Strategic Value
Healthcare & Sensitive Records Protection
Implement end-to-end encryption and audit logging to protect confidential patient and user data.
 03
Application Scope
Enterprise Cloud Workload Defense
Strategic Value
Enterprise Cloud Workload Defense
Harden Kubernetes clusters, VPC configurations, and serverless compute against privilege escalation and data exfiltration.
FAQ
Frequently Asked Questions About Cybersecurity & Cloud Protection
Find clear answers about our Cybersecurity & Cloud Protection capabilities, engagement models, engineering team, and post-launch SLAs.
How often should our company perform penetration testing?
Industry standards recommend thorough third-party penetration testing at least annually, or whenever significant architectural changes are deployed to production.
Do you help us achieve SOC 2 or ISO 27001 certifications?
Yes, our security engineers implement the exact technical controls, access policies, and audit trails required by certification assessors.
Will penetration testing cause disruption to our live users?
No, we carefully coordinate test execution, utilizing staging replicas or controlled traffic throttles to avoid any disruption to production services.
What deliverable do we receive upon test completion?
You receive an executive summary for stakeholders, an audit-ready compliance document, and a detailed technical report with exact steps to remediate each finding.
✦
Let's build together
Ready to create your Cybersecurity & Cloud Protection experience?
Tell us about your technical roadmap and our engineering leadership will get back to you with a concrete plan.